

Cybersecurity services for Oklahoma businesses
Including risk assessments, threat monitoring, compliance support, and security management.
Cybersecurity isn’t about checking boxes. It’s about understanding how an attacker could target your business and taking action before they do. Our assessments deliver an honest evaluation of your security posture, prioritized recommendations, and a practical plan for reducing risk.
Cybersecurity services we deliver for every client
For more than 20 years, we’ve helped Oklahoma SMBs strengthen their cybersecurity, reduce risk, and stay protected in an evolving threat landscape.
Security monitoring & incident response
We continuously monitor your environment for suspicious activity, security alerts, and indicators of compromise. When a threat is detected, we investigate, contain, and respond according to the severity of the incident.
Dark web & credential monitoring
We monitor dark web sources, breach databases, and exposed credential repositories for compromised passwords, company domains, and sensitive business information.
Third-party risk management
Your security is only as strong as the vendors connected to your business. We assess vendor security practices, identify third-party risks, and help ensure critical partners meet appropriate security standards.
Vulnerability management
We identify security vulnerabilities across operating systems, applications, cloud environments, and third-party platforms, then prioritize remediation based on risk.
Security policies & governance
We develop, maintain, and enforce security policies, procedures, and standards that align with your business operations, compliance requirements, and risk tolerance.
Security awareness training
Employees remain one of the most common attack vectors. We provide ongoing security awareness and phishing training that helps your staff recognize and respond to real-world threats.
Identity & access management
We secure user access through multi-factor authentication (MFA), role-based access controls, privileged account management, and identity governance best practices.
Data protection & encryption
We protect sensitive data through encryption, access controls, data classification, and secure storage practices for data at rest, in transit, and across cloud environments.

The 30-day cybersecurity risk assessment
Thirty days. Nine areas. One written report on where you stand, what needs attention, and what to address first.
01
Internal scans
We find the weak spots inside your network.
02
External testing
We show you what an attacker sees from the outside.
03
Vendor risk review
We check the outside companies that have access to your data.
04
Configuration audit
We verify your systems are set up to security standards.
05
Policy review
We check whether your policies match how your team actually works.
06
Access review
We confirm the right people have the right access, and that old accounts are gone.
07
Security maturity scoring
We score security across every layer of your infrastructure and identify the highest-risk areas.
08
Compliance assessment
We measure your organization against HIPAA, CMMC, SOC 2, PCI, or other applicable requirements.
09
Prioritized plan
We tell you what to fix first based on actual risk, not on what costs the most.

“I spent years watching how attacks actually work. That’s why we assess before you sign anything.”
– Cory Carson, Founder & CEO
Cybersecurity is an ongoing process

Assessment
Thirty days across nine areas. You get a written report, and it’s yours whether you hire us or not.

Implementation
We fix what the report found, starting with what reduces the most risk.

Ongoing protection
Monitoring, training, and policy work, handled by the same people who ran your assessment.
Cybersecurity that connects to CMMC, HIPAA, SOC 2, and PCI
For Oklahoma businesses in regulated industries, security is not only about avoiding a breach. It is about meeting the requirements that let you keep doing business.
CMMC for defense contractors. HIPAA for medical practices. SOC 2 for financial services. PCI for anyone taking card payments. We build for compliance from the start. When we design your security, we document the controls, the procedures, and the audit trails a reviewer will ask for.
See our compliance services for how each framework works.

Common questions about cybersecurity
What is a cybersecurity risk assessment?
It is a review of your technology to find weak spots, check where you stand on compliance, and rank what needs fixing. Ours runs for 30 days and covers nine areas. You end up with a written report and a recommended plan.
What does the assessment cost?
It depends on how many people are on your team. Schedule a short call and we will give you a number on the call, not after a discovery process.
What happens after the 30 days? Do I have to buy anything?
Nothing is automatic. The report is yours. If you want us to do the remediation work, we will scope it separately. If you want to hand the report to someone else, or handle it in house, that is fine too.
What if the report says we are mostly fine?
Then we tell you that. It happens. You still get the report, and you still know where your gaps are. We would rather give you an honest picture than sell you tools you do not need.
Which compliance frameworks can you help with?
CMMC, HIPAA, SOC 2, and PCI. Our security work is built to support these from day one, so you are ready when a deadline arrives rather than scrambling.
If you work on defense contracts, see our CMMC compliance services.
What is included in ongoing cybersecurity services?
Threat monitoring, policy development and enforcement, employee training, dark web monitoring, password and identity management, data encryption, third-party tool monitoring, and vendor oversight.
What we prioritize depends on your industry and your requirements.
What size business do you work with?
Most of our clients have between 10 and 250 employees.
Below that, a business usually needs less than we are built to deliver, and we will tell you that rather than sell you something you do not need.
Do you work with businesses outside Oklahoma City and Tulsa?
Yes. We are based in Oklahoma, and our teams serve the OKC and Tulsa metros, and we work with businesses across the state.
Thirty years of security experience, delivered locally
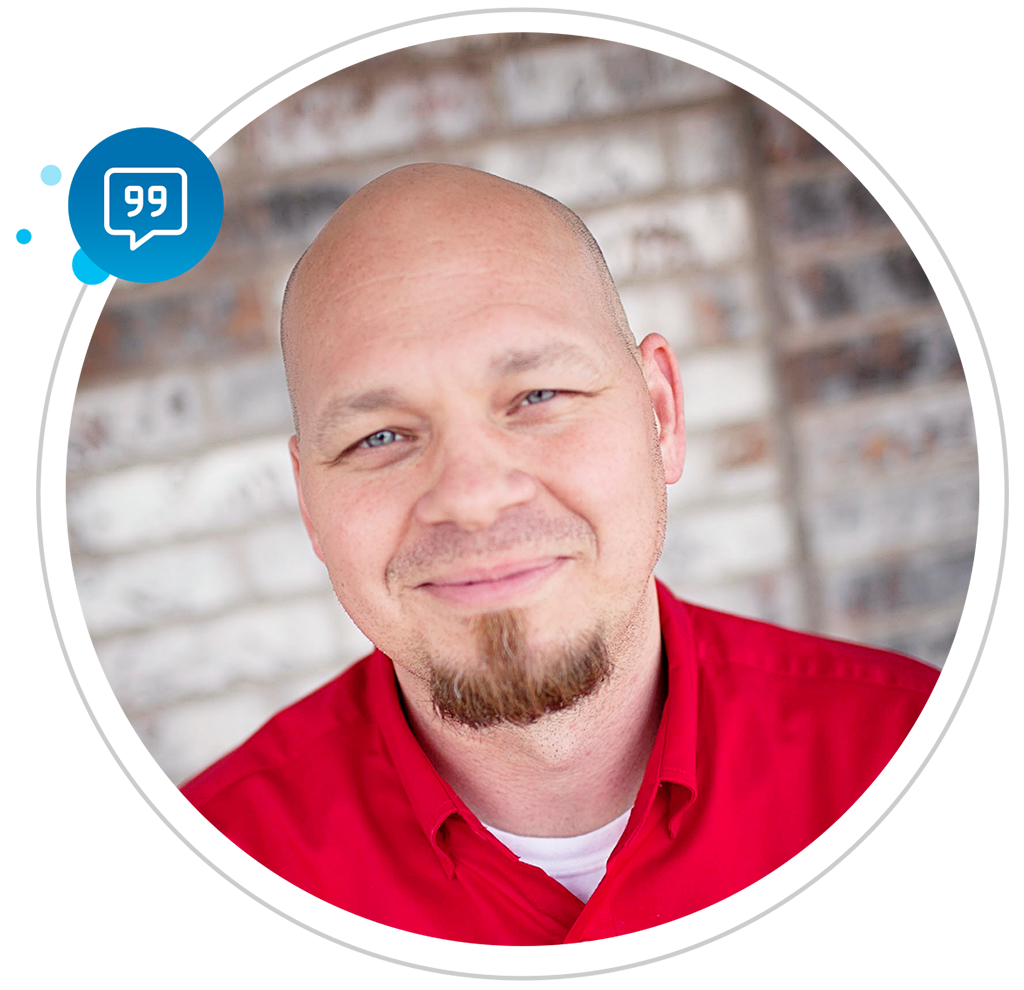
Our founder, Cory Carson, has spent nearly 30 years in technology and security. He built his career at America Online in technical security roles, supporting large-scale cybersecurity work alongside federal agencies, including the FBI and Homeland Security.
Real security takes more than tools. It takes someone who understands how attacks actually work.
Get a Quote


Have questions? Let's talk.
Ask questions, explore options, and learn what's possible for your business.